
One platform for network and security, run for you.
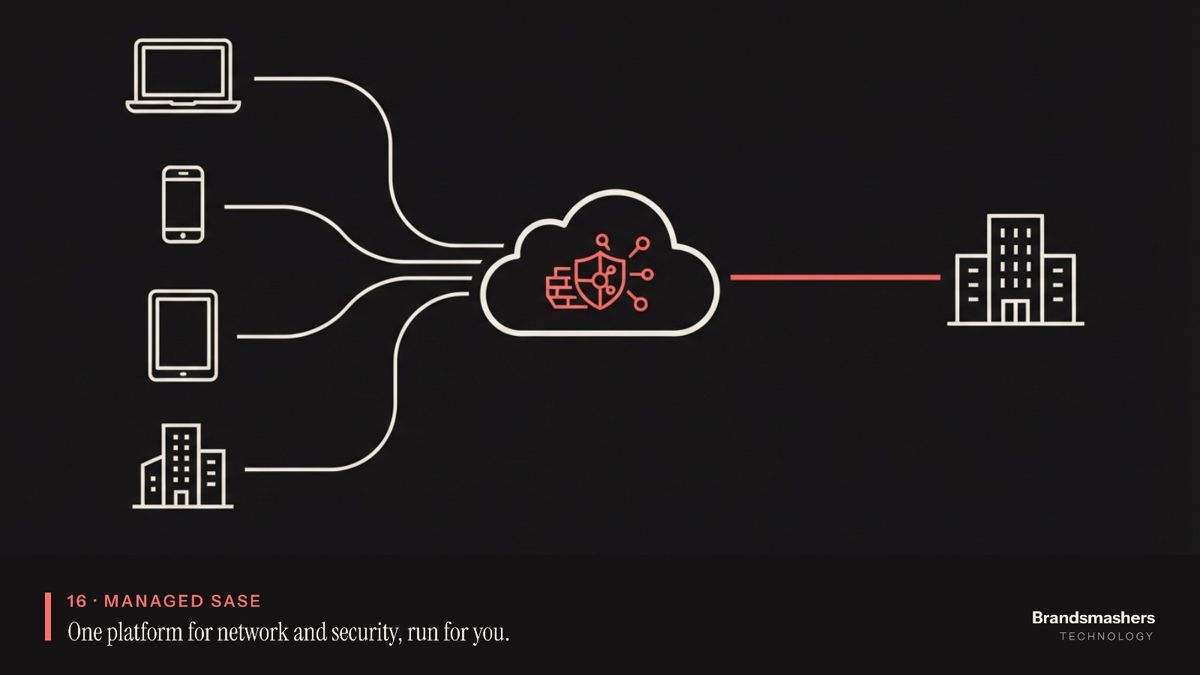
We design, migrate and operate SASE so a hybrid workforce gets secure access without a VPN.
- 48–72 HOURS
- TOP 3% ENGINEERS
- 100% REPLACEMENT
What we do.
Assessment
of your current network, VPN and security tooling: traffic paths, apps, users, sites and contracts.
SASE design
secure web gateway, zero trust network access (ZTNA), firewall-as-a-service and SD-WAN, matched to your sites and risk.
Phased migration with user communication,
so people know what changes and when.
24/7 monitoring and policy management,
with a named team that tunes rules and handles alerts.
Cost consolidation
of overlapping tools, with a plan for contracts as they come up for renewal.
How we work.
We begin by learning what actually runs on your network. Then we design the target and pick a pilot group. We migrate in waves, by site or by team, never all at once. Each wave has a rollback plan. We write short guides, brief managers and keep a help channel open. After the last wave, we run a stabilisation period, tune policy against real traffic and move into managed operations with regular reviews.
Who this is for.
IT leaders whose VPN is slow, overloaded and the top source of support tickets.
Companies with several sites and a hybrid workforce who want the same protection everywhere.
Security teams running multiple point tools with separate policies and gaps between them.
Firms preparing for a firewall or VPN hardware refresh who would rather not buy more appliances.
Teams without 24/7 security cover who want an operator on call.
What you get.
A current-state assessment and a target design.
A tool and contract consolidation plan.
A configured SASE platform with unified policy.
ZTNA access to your internal and cloud apps, replacing the VPN where possible.
A pilot, phased rollout and user communication pack.
Monitoring, alert handling and policy change management.
Regular reports on traffic, incidents and tickets, plus runbooks.
- Top 3% of applicants
- Start in 48–72 hours
- Dedicated account manager
- 100% replacement guarantee
Typical timeline.
Timing depends on the number of sites, the state of your apps and how many legacy exceptions exist.
- 01
Weeks 1 to 2
discovery and assessment, traffic and app inventory.
- 02
Weeks 3 to 4
design, platform setup and pilot group.
- 03
Weeks 5 to 7
phased rollout, site by site or team by team.
- 04
Week 8
stabilisation, policy tuning and VPN retirement planning.
- 05
After that
managed operations and quarterly reviews.
Proof
A mid-market company with 350 users across 5 sites completed migration in 55 days and cut VPN-related tickets by 32%. A mid-market B2B services company retired 2 legacy tools and cut ongoing licence costs by 18%. Our engineers join your standup within 72 hours, and about 3% of applicants pass our 4-gate vetting.
No. Most migrations run both side by side. Apps move to zero trust access in waves, and the VPN is turned off when nothing depends on it.
Related work and reading.
 Case studyMigrating a hybrid workforce to managed SASE in under 60 daysRead the story
 Case studyConsolidating network and security into one SASE platformRead the story
 ArticleSASE explained: why it's hitting a tipping point in 2026Read the article
 ArticleIs your VPN setup quietly putting you at risk?Read the article
LET'S TALK. Start now.
Tell us what you're building. We'll come back with a plan and matched, pre-vetted engineers.
CONTACT