
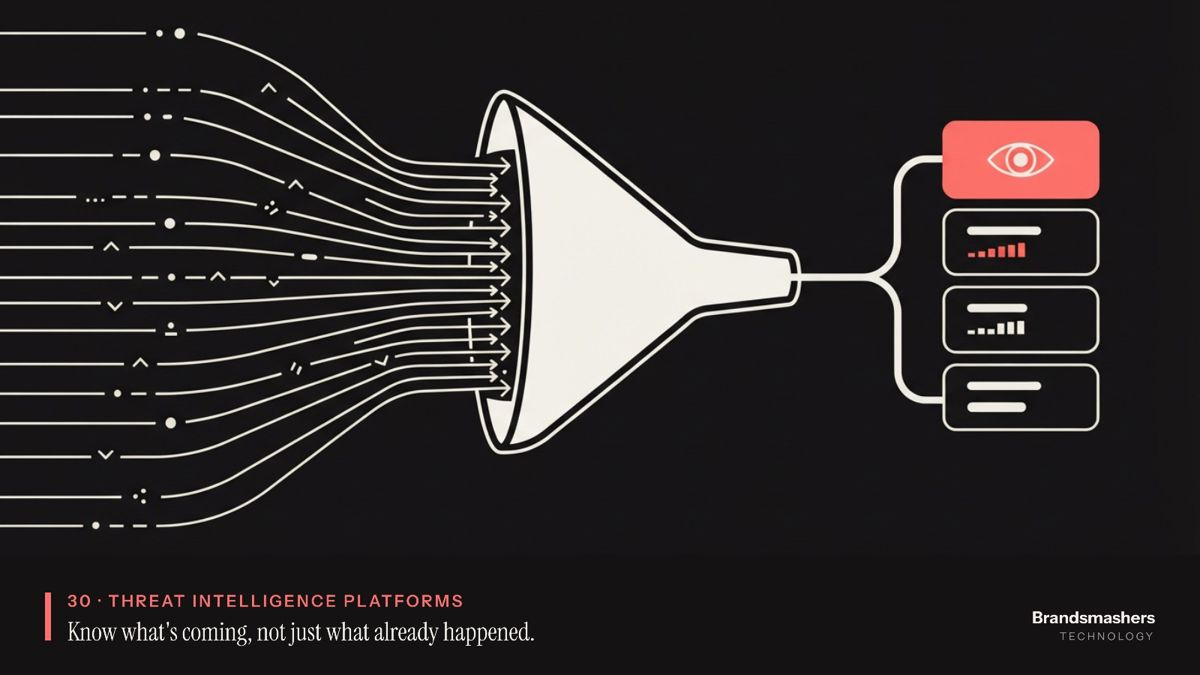
Know what's coming, not just what already happened.
Feed aggregation, enrichment, scoring and threat-hunting workflows for MSSPs and security teams, built by senior engineers who understand how analysts actually work.
- 48–72 HOURS
- TOP 3% ENGINEERS
- 100% REPLACEMENT
Most security tooling tells you about an event after it has happened. Meanwhile your analysts are buried in feeds, reports and alerts from a dozen sources, many of them repeating each other. The information needed to prepare is usually already available. What is missing is a platform that gathers it, cleans it, ranks it against your own environment and puts it in front of the right person. That is an engineering problem, and it is one we solve.
- 48–72hfrom first call to engineers in your standup
- Top 3%of applicants, vetted for the work
- 100%replacement guarantee on every hire
What we do.
Aggregate commercial, open-source and internal threat feeds.
Connectors for the formats you receive, such as STIX and TAXII, CSV, JSON and email, with clear handling of rate limits, outages and licence terms.
Enrich and deduplicate indicators; score relevance.
Normalise indicators, merge duplicates, add context such as geolocation, first-seen dates and related campaigns, and score each one against your assets and industry. Scoring rules are written down and visible to analysts.
Integrate with SIEM, SOAR and EDR.
Push scored indicators to detection tools and pull back sightings, so intelligence and telemetry meet in one place.
Threat hunting workflows and reporting.
Hypothesis-driven hunts, saved queries, case notes and reports for leadership and customers.
Multi-tenant platforms for MSSPs.
Strict separation of client data, per-tenant scoring and role-based access, so one platform serves many customers safely.
Who this is for.
An MSSP whose analysts spend the first hour of each shift sorting duplicate indicators.
A security team that buys several feeds and cannot say which of them is worth the money.
A company with a SIEM full of rules and no systematic way to decide what to hunt for.
A founder building a threat intelligence product who needs a senior team to ship the first version.
A mid-sized firm with no dedicated security staff that wants proactive coverage without hiring a full team.
How we work.
Start with the analyst.
We sit with the people who triage and hunt, and map their day before designing anything.
Pick the feeds that matter.
We audit what you receive, measure overlap and usefulness, and drop the noise.
Build a thin pipeline first.
Ingest, deduplicate, enrich, score, deliver. One end-to-end path before breadth.
Keep scoring transparent.
Every score shows the reasons behind it. Analysts can challenge a rule and change it.
Hand over properly.
Documentation, runbooks and an on-call period while your team takes over.
What you get.
A working pipeline with connectors for your chosen feeds.
A normalised indicator store with deduplication and enrichment.
A scoring model your analysts can read and adjust.
Integrations with your SIEM, SOAR and EDR tools.
Hunt queries, response playbooks and reporting templates.
Monitoring on the platform itself, so you know when a feed goes quiet.
- Top 3% of applicants
- Start in 48–72 hours
- Dedicated account manager
- 100% replacement guarantee
Typical timeline.
- 01
Weeks 1 to 2
discovery, feed audit, architecture and success measures.
- 02
Weeks 3 to 6
core pipeline, first connectors, enrichment and an initial scoring model.
- 03
Weeks 7 to 9
integrations, analyst interface and first hunting workflows.
- 04
Weeks 10 to 12
tuning with live data, reporting, hardening and handover. Multi-tenant builds take longer.
Proof
For a managed security provider we built a feed aggregation pipeline that cut alert noise by 40% and helped analysts triage about 30% faster.
No. We build the platform that takes in the feeds you choose or already own. We are independent of any feed vendor.
Related work and reading.
 Case studyBuilding a threat intelligence feed aggregator for an MSSPRead the story
 Case studyStanding up proactive threat hunting for a client with no security teamRead the story
 ArticleWhy reactive security isn't enough anymoreRead the article
 ArticleThreat intelligence 101: what it is and who needs itRead the article
LET'S TALK. Start now.
Tell us what you're building. We'll come back with a plan and matched, pre-vetted engineers.
CONTACT