
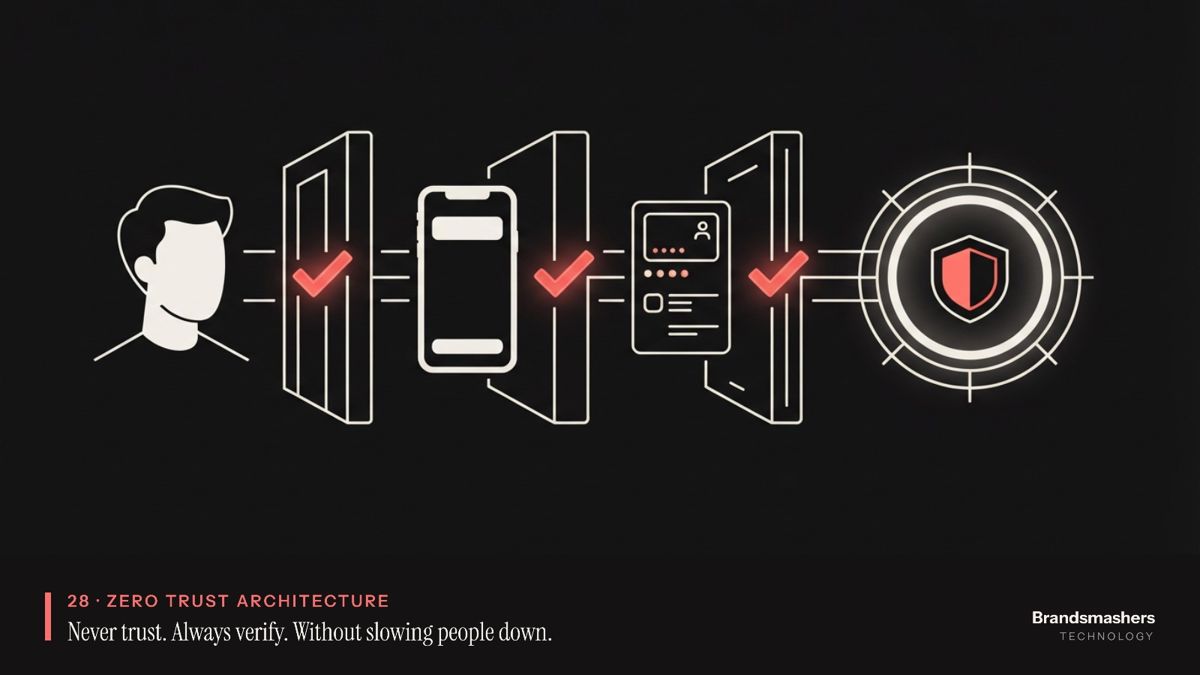
Never trust. Always verify. Without slowing people down.
We design and roll out zero-trust access for distributed teams, cloud and legacy apps.
- 48–72 HOURS
- TOP 3% ENGINEERS
- 100% REPLACEMENT
What we do.
Current-state assessment and roadmap.
We map users, devices, apps, data and existing controls, then agree a sequence of steps ranked by risk and effort.
Identity-centric access (SSO, MFA, device posture).
Single sign-on, strong multi-factor authentication and checks on the health and ownership of the device before access is granted.
Micro-segmentation and least privilege.
Smaller access zones and role-based policies, so a user or system can reach only what it needs.
Continuous verification and monitoring.
Session checks, risk signals and logging that feed your security team, so odd behaviour is seen quickly.
Phased rollout with user support.
Pilot groups, clear communication, a help channel and a rollback plan for each phase.
Who this is for.
A mid-market company still relying on a VPN that gives staff broad access to the internal network.
A security lead asked to show progress on zero trust but unsure where to start.
An enterprise with flat internal access, legacy apps and a board that has asked about breach impact.
A distributed team using many SaaS and cloud tools, each with its own login and rules.
An IT team buried in access tickets and exceptions that nobody can explain.
How we work.
We begin by learning what exists. We list apps, users, groups and devices, and observe real traffic for a period. Many policy mistakes come from guessing who uses what, so we measure first.
We then protect the most sensitive applications and the most privileged users. Early wins matter, because they build trust with users and leadership. Each phase starts with a small pilot group, moves to a wider group, then to everyone.
Users are part of the design. We write plain guidance, run short sessions and keep a support channel open during each rollout. When a policy blocks legitimate work, we adjust it quickly and record why.
What you get.
A current-state assessment and a prioritised roadmap with owners and measures.
Identity setup: SSO, MFA policy and conditional access rules.
Device posture checks tied to access decisions.
Segmentation design and policies for the applications in scope.
Logging and monitoring feeds into your existing security tooling.
Rollout plans, user communications and support runbooks.
Before and after network diagrams, plus a handover to your team.
- Top 3% of applicants
- Start in 48–72 hours
- Dedicated account manager
- 100% replacement guarantee
Typical timeline.
Timelines depend on the number of legacy apps and on how clean your identity data is.
- 01
Weeks 1 to 3
Assessment. Inventory, traffic discovery, risk ranking and roadmap.
- 02
Weeks 4 to 7
Identity foundation. SSO, MFA and device checks, with a pilot group.
- 03
Weeks 8 to 14
Application access. Move the first set of apps behind identity-based access, with policies in monitor mode first.
- 04
Weeks 15 to 24
Wider rollout, segmentation of sensitive systems, VPN reduction and handover.
Proof
For an anonymised mid-market company with 350 users, a phased rollout retired the VPN for 90% of apps and cut access-related tickets by 30%. Brandsmashers has deployed 150+ developers, and about 3% of applicants pass our 4-gate vetting.
It should not. Good zero trust removes steps people dislike, such as manual VPN connections, and asks for stronger checks only when risk is higher.
Related work and reading.
 Case studyA zero trust network rollout for a distributed workforceRead the story
 Case studyReplacing implicit trust with continuous verification for an enterprise clientRead the story
 ArticleZero trust explained without the marketing jargonRead the article
 ArticleWhy 'trust but verify' isn't good enough anymoreRead the article
LET'S TALK. Start now.
Tell us what you're building. We'll come back with a plan and matched, pre-vetted engineers.
CONTACT