
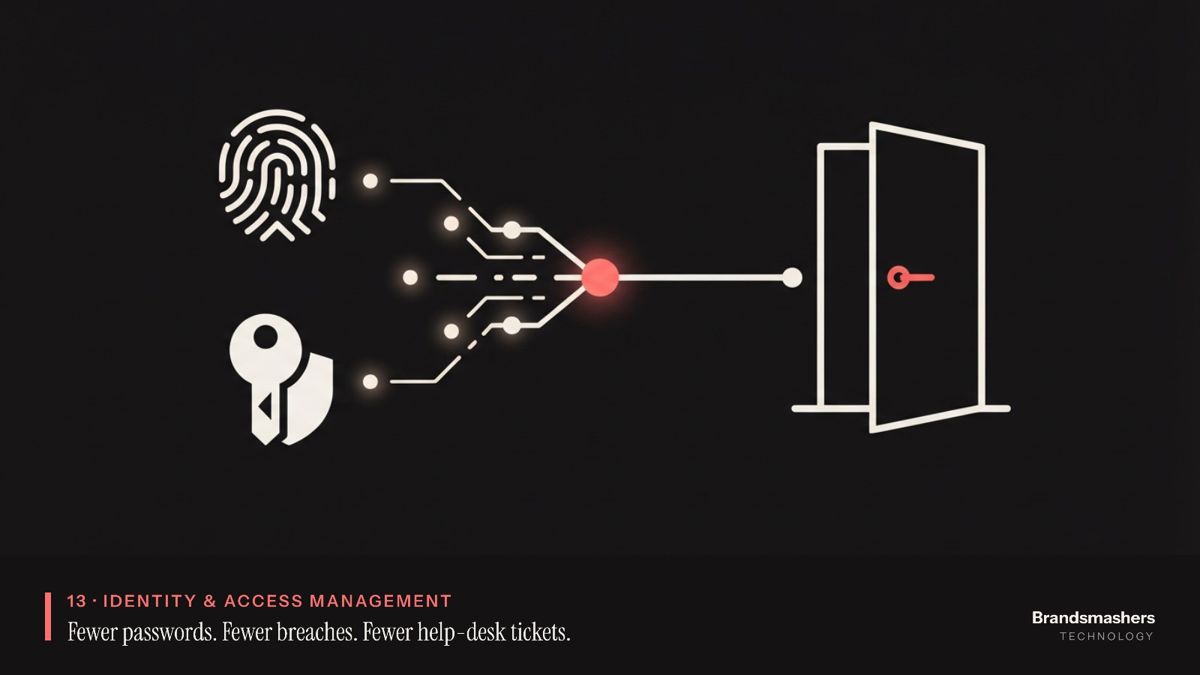
Fewer passwords. Fewer breaches. Fewer help-desk tickets.
We design and roll out identity platforms, single sign-on and passwordless authentication, so people sign in faster and attackers have less to steal.
- 48–72 HOURS
- TOP 3% ENGINEERS
- 100% REPLACEMENT
What we do.
Passwordless rollout
passkeys, authenticator apps and hardware keys, chosen by user group and device, with a fallback that is safe and not a back door.
Single sign-on and multi-factor authentication
across your business apps, including the older ones that were never built for either.
Identity consolidation
we map accounts from several directories into one source of truth, clean duplicates and move apps over in order.
Role-based access, joiner-mover-leaver automation and access reviews,
so access follows the person's job and ends when the job does.
Privileged access controls
for admins and service accounts, including vaulting, short-lived elevation and logging.
How we work.
We start with an inventory: directories, apps, auth methods, admin accounts and service accounts. Then we agree a target design and a phased plan. We pilot with IT first, then one department, then the rest. Every phase has a rollback. We train users with short, plain guides and run a visible help channel during each wave. After go-live we hand over runbooks and stay on for stabilisation.
Who this is for.
IT heads whose help desk spends too much time on password resets and lockouts.
Companies that grew through acquisitions and now run several directories with different rules.
Security leads who know leavers and old admin accounts are still active but cannot prove how many.
Firms facing a customer security review or audit that asks for MFA on every admin account.
Teams that bought an identity platform and only half deployed it.
What you get.
A current-state report of identities, apps and gaps, ranked by risk.
A target architecture and a phased rollout plan.
A working SSO and MFA or passkey setup, configured and tested.
Automated joiner-mover-leaver flows tied to your HR source.
Role definitions and a first access review, with owners named.
Admin and service account controls with logging.
User guides, a help-desk script and handover runbooks.
- Top 3% of applicants
- Start in 48–72 hours
- Dedicated account manager
- 100% replacement guarantee
Typical timeline.
Scope changes this. A single directory and thirty apps is quicker than five directories and a legacy estate.
- 01
Weeks 1 to 2
discovery and inventory, risk ranking, target design.
- 02
Weeks 3 to 5
build the platform, connect the directory, pilot with IT.
- 03
Weeks 6 to 10
expand department by department, train users, move apps to SSO.
- 04
Weeks 11 to 14
retire passwords app by app, tighten admin access, run the first access review.
- 05
After that
stabilisation, metrics and handover.
Proof
In one engagement, a 500-person enterprise reached 92% passkey adoption in 90 days and cut password-reset tickets by 40%. In another, we removed 140 dormant accounts and cut onboarding from 2 days to 4 hours. Our engineers join your standup within 72 hours, and about 3% of applicants pass our 4-gate vetting.
No, if the fallback is planned. We set up recovery with a second device, a hardware key held by IT or an identity check by the help desk. We test each path before rollout.
Related work and reading.
 Case studyRolling out passwordless authentication across a 500-person enterpriseRead the story
 Case studyConsolidating five identity systems into one IAM platformRead the story
 ArticlePasswordless isn't the future anymore. It's the baselineRead the article
 ArticleIAM mistakes that lead to the most preventable breachesRead the article
LET'S TALK. Start now.
Tell us what you're building. We'll come back with a plan and matched, pre-vetted engineers.
CONTACT