
Know exactly what's inside your software.
SBOM generation, dependency risk monitoring and secure build pipelines, run by senior engineers who have done it on real codebases.
- 48–72 HOURS
- TOP 3% ENGINEERS
- 100% REPLACEMENT
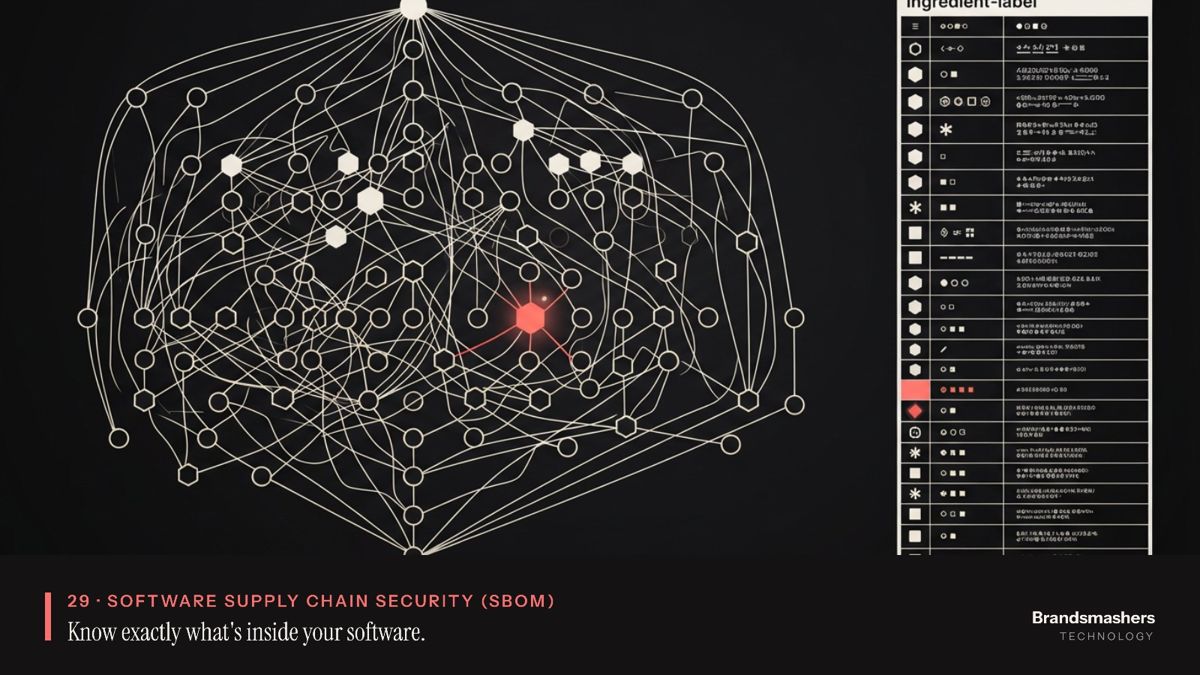
Most of the code you ship was written by someone else. When a serious flaw in a popular package is announced, the first question is simple: are we affected? Most teams cannot answer it quickly. Customers and some regulations are also starting to ask for a software bill of materials, so the inventory is becoming a sales and compliance requirement as well as a security one. Building it once, properly, is cheaper than answering every request by hand.
- 48–72hfrom first call to engineers in your standup
- Top 3%of applicants, vetted for the work
- 100%replacement guarantee on every hire
What we do.
SBOM generation (SPDX, CycloneDX) across repositories.
Produced in CI on every build, so the inventory is never stale, and stored where security and sales can both find it.
Dependency vulnerability and licence monitoring.
Continuous scanning against public advisories, with findings routed to the team that owns the code.
Build pipeline hardening and signing.
Locked-down runners, pinned actions and base images, signed artefacts and provenance records.
Policies to block risky dependencies.
Clear rules for what may and may not enter a build, enforced automatically, with a written exception process.
Support for customer and regulator SBOM requests.
A repeatable way to produce, review and deliver an SBOM when a questionnaire or contract asks for one.
Who this is for.
A CTO who has been asked by an enterprise customer for an SBOM and has nothing to send.
A security lead who cannot say which services use a package named in this morning's advisory.
An engineering manager with dozens of repositories, several package managers and no shared view of them.
A company preparing for an audit or procurement review that asks about third-party components and licences.
A team that wants release gates for dependencies but fears slowing down delivery.
How we work.
Inventory first.
We find every repository, language and package manager before we write any tooling.
Automate in CI.
SBOM generation and scanning run as pipeline steps your developers already see.
Triage with owners.
Each finding gets a named owner, a severity and a due date. Noise is tuned out early.
Gate gradually.
We start in report-only mode, then block only what the team agrees is worth blocking.
Hand over.
Your engineers run it. We document it and stay on call while it settles.
What you get.
Working SBOM generation in your pipelines, in the formats your customers ask for.
A searchable inventory that answers "are we affected?" without a meeting.
A dependency policy and the release gates that enforce it.
A remediation workflow with owners, severities and due dates.
Hardened, signed builds with a short runbook.
A template for answering customer and regulator SBOM requests.
- Top 3% of applicants
- Start in 48–72 hours
- Dedicated account manager
- 100% replacement guarantee
Typical timeline.
- 01
Weeks 1 to 2
repository discovery, tooling choice, a pilot on two or three repositories.
- 02
Weeks 3 to 5
roll-out of SBOM generation and scanning across priority repositories.
- 03
Weeks 6 to 7
triage, policy design, report-only gates.
- 04
Week 8 onward
enforcement, pipeline hardening and handover. Larger estates take longer.
Proof
Across 60 repositories for a mid-market B2B services company, we got 92% of priority repositories covered and cut the time to answer "are we affected?" from days to under an hour.
Both SPDX and CycloneDX are widely accepted. We usually generate whichever your customers request and can produce both from the same data.
Related work and reading.
 Case studyGenerating and managing SBOMs across a client's entire codebaseRead the story
 Case studyCatching a vulnerable dependency before it reached productionRead the story
 ArticleWhat an SBOM is and why regulators are starting to ask for oneRead the article
 ArticleThe hidden risk living inside your open-source dependenciesRead the article
LET'S TALK. Start now.
Tell us what you're building. We'll come back with a plan and matched, pre-vetted engineers.
CONTACT